SECURITY OPERATIONS CENTER (SOC)
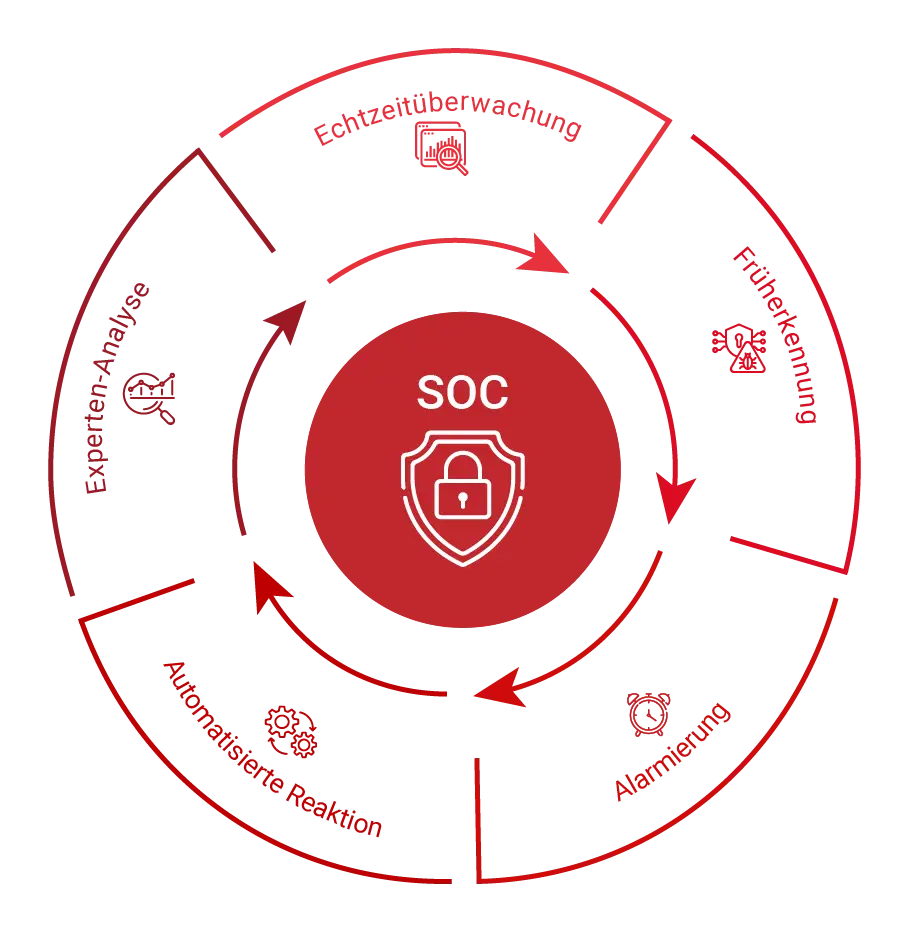
How can cyber threats be detected?
Why is a Security Operations Center important for businesses?
IT environments are becoming increasingly complex due to cloud services, mobile workplaces, and networked systems, offering a growing attack surface for cyberattacks. Furthermore, this increasing complexity makes it more difficult for companies to continuously monitor their entire IT infrastructure and identify security risks. A Security Operations Center (SOC) monitors IT systems and detects potential cyber threats early on. Through continuous security monitoring, suspicious activity is identified before a serious incident occurs. A SOC thus minimizes the risk of a successful cyberattack on your company.
Our offer: redIT SOC
SOC as a Service Switzerland
- Effective protection and monitoring of the IT infrastructure
- Predefined automatic countermeasures in case of incident
- Automatic reporting of a security incident
- Detection of attack patterns
- Evaluation of alarm messages by our redIT specialists during redIT operating hours
24/7 monitoring, automation and redIT Expertise
Endpoint & Cloud SOC
from CHF 210.00 / month
- Onboarding
- Endpoint Security Monitoring
- Microsoft 365 & Entra ID
- Analysis and prioritization
- Recommendations for action
- Alarm Triage
IoT / OT (NDR) SOC
Price on request
- Onboarding
- IoT/OT network monitoring
- Analysis and prioritization
- Recommendations for action
- Alarm Triage
M365 Light SOC
from CHF 100.00 / month
- Onboarding
- Microsoft 365 & Entra ID Monitoring
- Analysis and prioritization
- Recommendations for action
- Alarm Triage
Perimeter SOC
from CHF 125.00 / month
- Onboarding
- Firewall Security Monitoring
- Analysis and prioritization
- Recommendations for action
- Alarm Triage
* All modules are also available individually and can be freely combined.
Perimeter SOC
M365 Light SOC
Endpoint & Cloud SOC
IoT/OT SOC
Network Connector
Level 1 – Essential
Small and medium-sized enterprises (SMEs) with few employees
Can be used individually: Cost-effective entry into 24/7 security monitoring
Modules
Perimeter SOC
from CHF 125.00 / month
M365 Light SOC
from CHF 100.00 / month
Level 2 – Basic
Small to medium-sized SMEs
Tailored combination: Clients, servers & cloud as well as network and perimeter infrastructure fully covered.
Modules
Perimeter SOC
from CHF 125.00 / month
Endpoint & Cloud SOC
from CHF 210.00 / month
Level 3 – Standard
Larger SMEs
Comprehensive monitoring of endpoints, identities, cloud services, IoT/OT, as well as network and perimeter.
Modules
Perimeter SOC
from CHF 125.00 / month
Endpoint & Cloud SOC
from CHF 210.00 / month
IoT/OT network-based SOC
Price on request
Level 4 – Extended
SMEs with the highest security requirements
Integration of vendor-independent sources for comprehensive and centralized monitoring of the entire IT infrastructure.
Modules
Perimeter SOC
from CHF 125.00 / month
Endpoint & Cloud SOC
from CHF 210.00 / month
IoT/OT network-based SOC
Price on request
Network Connector
Price on request
* The steps are for guidance only – modules can be used as needed.
Who is our Managed SOC suitable for?
redIT SOC is suitable for small, medium-sized, and large companies that have high demands on their IT security and want to professionally implement their security monitoring. The service is particularly well-suited for organizations that rely on modern technologies, clear processes, and the support of experienced security specialists.
Companies that want to further uncover and minimize their IT vulnerabilities also benefit from security assessments and vulnerability management.
This is how our SOC protects our customers

“ The collaboration with redIT was a crucial factor in our success. Thanks to their expertise and proactive support, we were able to improve our IT security and are proactively protected against potential attacks. ”
Marc Mueller
Head of ICT & Digitalization, BURRI public elements AG
The advantages of SOC

Protection against cyber threats
Your IT infrastructure is monitored around the clock. Threats are detected early and automatically isolated using predefined rules.

Recognize attack patterns early
The SOC detects suspicious activities and attack patterns early, assesses anomalies and automatically triggers an alarm if necessary.

Automated incident response
In the event of detected security incidents, appropriate countermeasures are immediately initiated for protection using defined automation rules.

Expert evaluation of alarms
Our security specialists evaluate incoming alarm notifications, analyze the situation and provide further support if necessary.

Cloud-based SOC solution
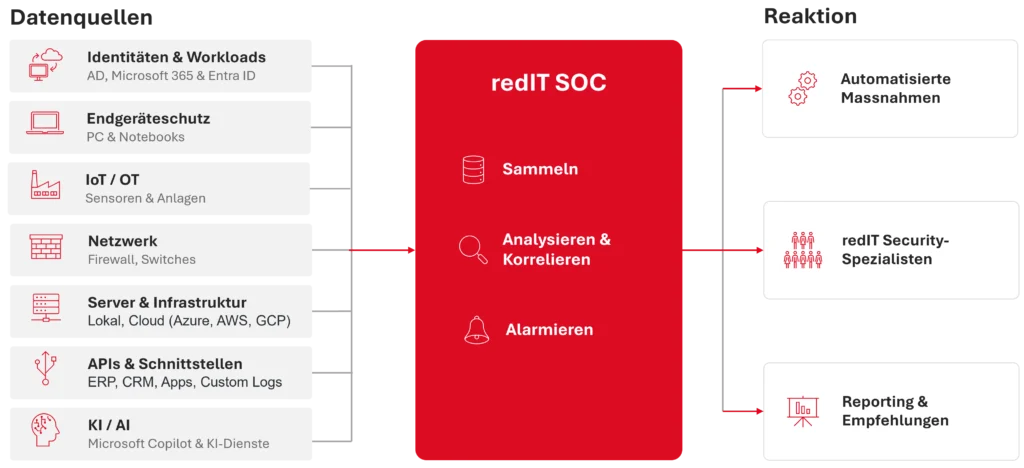
The cloud-based SOC solution enables centralized security monitoring without requiring additional local infrastructure.

Flexible thanks to modular building blocks
Thanks to its modular design, the SOC can be flexibly adapted to your requirements and expanded at any time should your needs change.
How does the redIT SOC work?
We help you take your IT security to the next level.
Do you want to know how well your IT is protected against cyberattacks today? Our security assessment provides an initial overview of risks and potential improvements.

Nicolas Portmann
Solution sales
+41 41 747 52 27
E-mail
Book an appointment online

Matthias De Toffol
Team Leader Cloud Services
Eastern location
+41 41 747 51 41
E-mail
The most important questions about the Security Operations Center (SOC)
What does Managed SOC mean?
In a managed SOC, the operation of the Security Operations Center is handled by a specialized service provider. Companies benefit from professional security monitoring without having to build their own SOC resources.
What are the advantages of a managed SOC?
- Early detection of threats
- Rapid response to security incidents
- Relieving the burden on internal IT
- Access to security specialists
- Continuous improvement of the security situation
- Transparency regarding risks and incidents
Why is security monitoring becoming increasingly important?
Is a Security Operations Center also useful for SMEs?
Yes. Small and medium-sized enterprises (SMEs) are increasingly becoming targets of cyberattacks. A Security Operations Center (SOC) helps to professionally monitor security risks and sustainably strengthen IT security. With SOC as a Service, SMEs benefit from experienced security experts without having to allocate their own, often limited, resources to building and operating a Security Operations Center.
How do the different modules differ?
The SOC modules monitor different areas of your IT infrastructure. Depending on the environment and security requirements, individual modules can be used or combined. This creates a SOC solution that is specifically tailored to your company's needs.
Which SOC modules does your company need?
Which SOC modules are suitable for your company depends on the company size , the IT environment, and the individual security and compliance requirements .